Zero Trust for NetBird
Zero Trust for NetBird
Make your NetBird network device-aware: only endpoints that meet your live posture baseline can reach CI runners, secrets, and internal apps — even if they’re authenticated.
Built for security teams protecting CI runners and internal services over NetBird.
The Risk
Your crown-jewel services are one device away from a breach.
Mesh VPNs like NetBird make access easy — but a stolen or compromised laptop with valid identity can still reach your runner, secrets, and internal apps. Credentials prove who, not whether the endpoint is safe right now.
Authenticated devices can still be unsafe (posture drift).
Malware turns an enrolled laptop into an attacker workstation.
CI runners and internal services become pivot points.
Device trust often covers login, not mesh access to internal IPs.
SECURITY GAP
The Device Trust Gap
VPN enrollment validates identity at join time. Access persists long after — even as endpoints drift out of posture.
Once an attacker is on an enrolled device, the mesh becomes their route to crown jewels. Continuous verification must happen in-network.
The Solution
Zero Trust, enforced at the mesh layer.
EDAMAME continuously checks device posture — not just enrollment — and keeps the NetBird group of compliant peers in sync. Your NetBird policies enforce; EDAMAME stays out of the traffic path.
Identity: each device joins with a work email and a one-time PIN.
Device policy: minimum score, required checks, compliance tags, AI allowlist.
Context: the NetBird peer identity, from laptops to CI runners.
Only devices that pass your policy stay in the NetBird group your access policies trust. Everything else is blocked — authenticated devices alone are no longer enough.
ARCHITECTURE
EDAMAME keeps a NetBird group in sync with your compliant devices, and your NetBird access policies decide what that group can reach — so crown jewels are only reachable from verified users on secure devices.
Device posture (EDAMAME Security or Posture) → EDAMAME Hub policy → NetBird group of compliant peers → NetBird enforces
No inline proxies. No custom tunnels. Just native enforcement inside your mesh.
Core Capabilities
Everything you need to secure NetBird without slowing your team down.
EDAMAME brings Zero Trust to your mesh — from laptops to CI runners — while keeping workflows fast and familiar.
Verified user identity
Each device joins your organization with a work email and a one-time PIN, so every peer in the group traces back to a real, verified person.
Continuous device posture
Enforce encryption, patches, EDR, firewall, and integrity. When a device reports out of policy, EDAMAME removes it from the NetBird group your access policies trust.
Native NetBird enforcement
Use a NetBird group in your access policies as the enforcement point. EDAMAME keeps its membership up to date based on live device posture.
Protect CI runners & internal services
Gate runner IPs, build agents, and admin surfaces behind posture-aware mesh access. A runner that reports out of policy leaves the NetBird group.
Team-friendly experience
Lightweight agents and clear remediation guidance. Engineers keep their tools and workflows — security runs in the background.
Works with your stack
Runs alongside your IdP, VPN, EDR and MDM, with enforcement through GitHub, GitLab, Entra ID, Google, NetBird, Tailscale, FortiGate and Netskope. No rip-and-replace.
Comparison
More than VPNs, mesh ACLs, or IP allowlists.
EDAMAME brings the on-prem rule to the cloud: reachable only from machines that meet your policy, with the speed and flexibility of modern cloud development.
Alternative
NetBird (default posture)
Once a device connects, it’s often trusted for too much. Posture is coarse, and internal services stay reachable even as endpoints drift.
With EDAMAME
Only devices that pass your policy stay in the NetBird group your ACLs grant. Drift out of compliance and the peer leaves the group at its next report.
Alternative
Network segmentation / bastions
Segmentation controls where, not whether an endpoint is safe right now. A compromised laptop inside the mesh can still pivot to runners and secrets.
With EDAMAME
Per-device enforcement inside the mesh. Each peer joins or leaves the NetBird group from its own posture reports.
Alternative
Static allowlists
Hard to maintain. User IPs change. No visibility into which device is behind an IP.
With EDAMAME
Per-device group membership from posture. Crown jewels are only reachable from peers that passed your policy at their last report.
Rollout
Five-minute rollout.
Enroll endpoints, connect NetBird, set your posture policy, and protect CI runners and internal apps — without redesigning networks.
Step 01
Install EDAMAME
Enroll laptops and workstations. Establish a baseline posture score.
Step 02
Connect your mesh
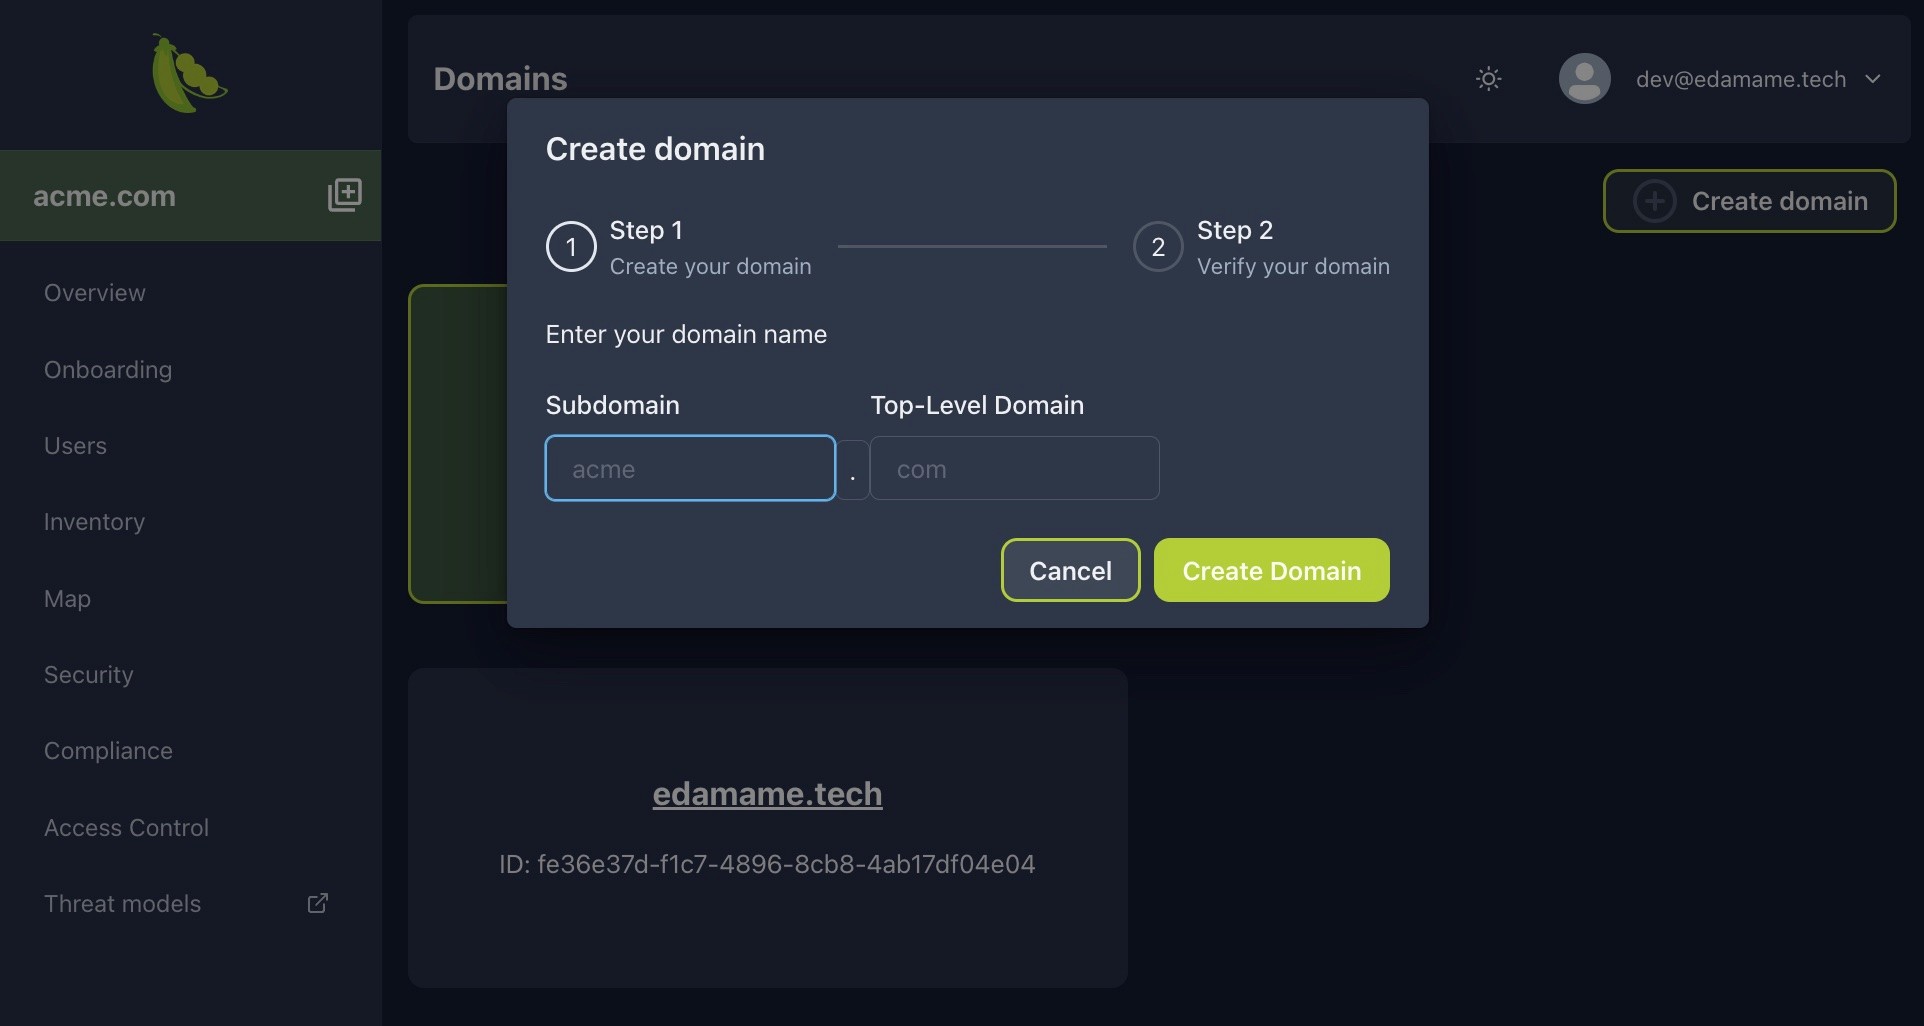
Paste a NetBird API token and group name into EDAMAME Hub. Peers are matched through the NetBird client on each device.
Step 03
Define posture policy
Set rules like score ≥ 4 and disk encryption enabled. Violations revoke access at the device’s next report.
Step 04
Protect crown jewels
Gate CI runners, secrets, and internal apps behind NetBird policies keyed on the EDAMAME-managed group.
Step 05
Expand coverage
Reuse the same posture policy across mesh access and SaaS (Entra / Google) for one control plane.
Threat Scenarios
Real attacks, blocked by design.
EDAMAME neutralizes the most common supply-chain and credential attack paths — before they reach your crown jewels.
Scenario
Stolen credentials
Without EDAMAME
Attacker uses the stolen credentials from any device to reach runners, secrets and internal apps.
With EDAMAME
A device outside the EDAMAME-managed group cannot reach your runners, secrets and internal apps, valid credentials or not.
Scenario
Compromised laptop
Without EDAMAME
Malware uses the laptop’s mesh access to reach runners, secrets and internal apps.
With EDAMAME
Posture deteriorates → the device reports it → EDAMAME removes it from the NetBird group → access granted through the group ends.
Scenario
Rogue CI/CD runner
Without EDAMAME
Malicious runner pulls secrets and injects backdoors into builds.
With EDAMAME
Runner fails posture → removed from the NetBird group, cut off from repos and secrets.
Trust & Impact
Security leaders choose EDAMAME to harden mesh access to their crown jewels.
Combine the assurance of air-gapped systems with the agility of a mesh VPN. EDAMAME lets you enforce Zero Trust on your NetBird network without sacrificing team velocity.
Stop rogue devices at the door — your NetBird network.
Strengthen SOC 2 and ISO 27001 compliance with continuous device-posture evidence.
Win your team’s trust by making security feel invisible.
A VPN gives you network isolation, but it doesn’t tell you whether the device itself should be trusted.
CTO
Telecom software company