Zero Trust for Entra ID
Zero Trust for Microsoft Entra ID
Close the token loophole: continuous identity, device, and context verification for every Microsoft 365 and Azure request — across web, desktop apps, and API.
Identity
Verified Developer
SSO-bound, trusted user
Platform
Microsoft Entra ID
Microsoft 365, Azure, Admin
Device
Secure Endpoint
Patches, EDR, encryption
Policy
EDAMAME Trust
Continuous access decisions
Blocks token-based attacks
Virtual air gap around your tenant
Developer-friendly rollout
Built for CTOs & CISOs securing Microsoft 365 and Azure.
The Risk
Your Microsoft tenant is one token away from a breach.
OAuth tokens, refresh tokens, and session cookies operate outside the login flow. A stolen token looks completely legitimate to Entra ID — no MFA check, no device verification. Compromised laptops and rogue CI runners can grant attackers full access to mailboxes, files, and Azure resources without re-triggering Conditional Access.
Stolen OAuth tokens and refresh tokens bypass identity and device checks.
Malware on a developer laptop turns it into an attacker workstation.
App / API / token access happens outside your login flow.
Traditional device trust covers login, not the Microsoft 365 operations that matter.
SECURITY GAP
The Token Loophole
Identity and device-trust tools validate posture at login. Entra ID grants access long after, using tokens and keys that never go back through those checks.
Once a token leaks, attackers can read mail, download files, and reach Azure resources from any device. With no continuous verification, the identity & device trust you paid for no longer applies.
The Solution
Zero Trust, enforced at the Entra ID layer.
Identity: SSO-bound, verified developer accounts.
Device: OS patches, encryption, EDR, firewall, and integrity checks.
Context: IP, environment, CI runner state, and access patterns.
EDAMAME continuously verifies the devices behind Microsoft 365 and Azure access — not just login. It keeps a trusted named location in sync with the public IPs of compliant devices, and your Conditional Access policy only grants access from there.
Only devices that pass your policy keep their IP in the named location. Everything else is blocked — tokens alone are no longer enough.
ARCHITECTURE
EDAMAME orchestrates Entra ID’s own security controls — Conditional Access named locations and dynamic IP allowlists — so that Microsoft itself only serves requests from verified users on secure devices.
Developer Device → EDAMAME Trust Engine → Microsoft Entra ID
No inline proxies. No custom tunnels. Just native enforcement at the point where it matters: your code platform.
Core Capabilities
Everything you need to secure Microsoft 365 without slowing developers.
EDAMAME brings Zero Trust principles to every machine that touches your code — from laptops to CI runners — while keeping workflows fast and familiar.
Verified developer identity
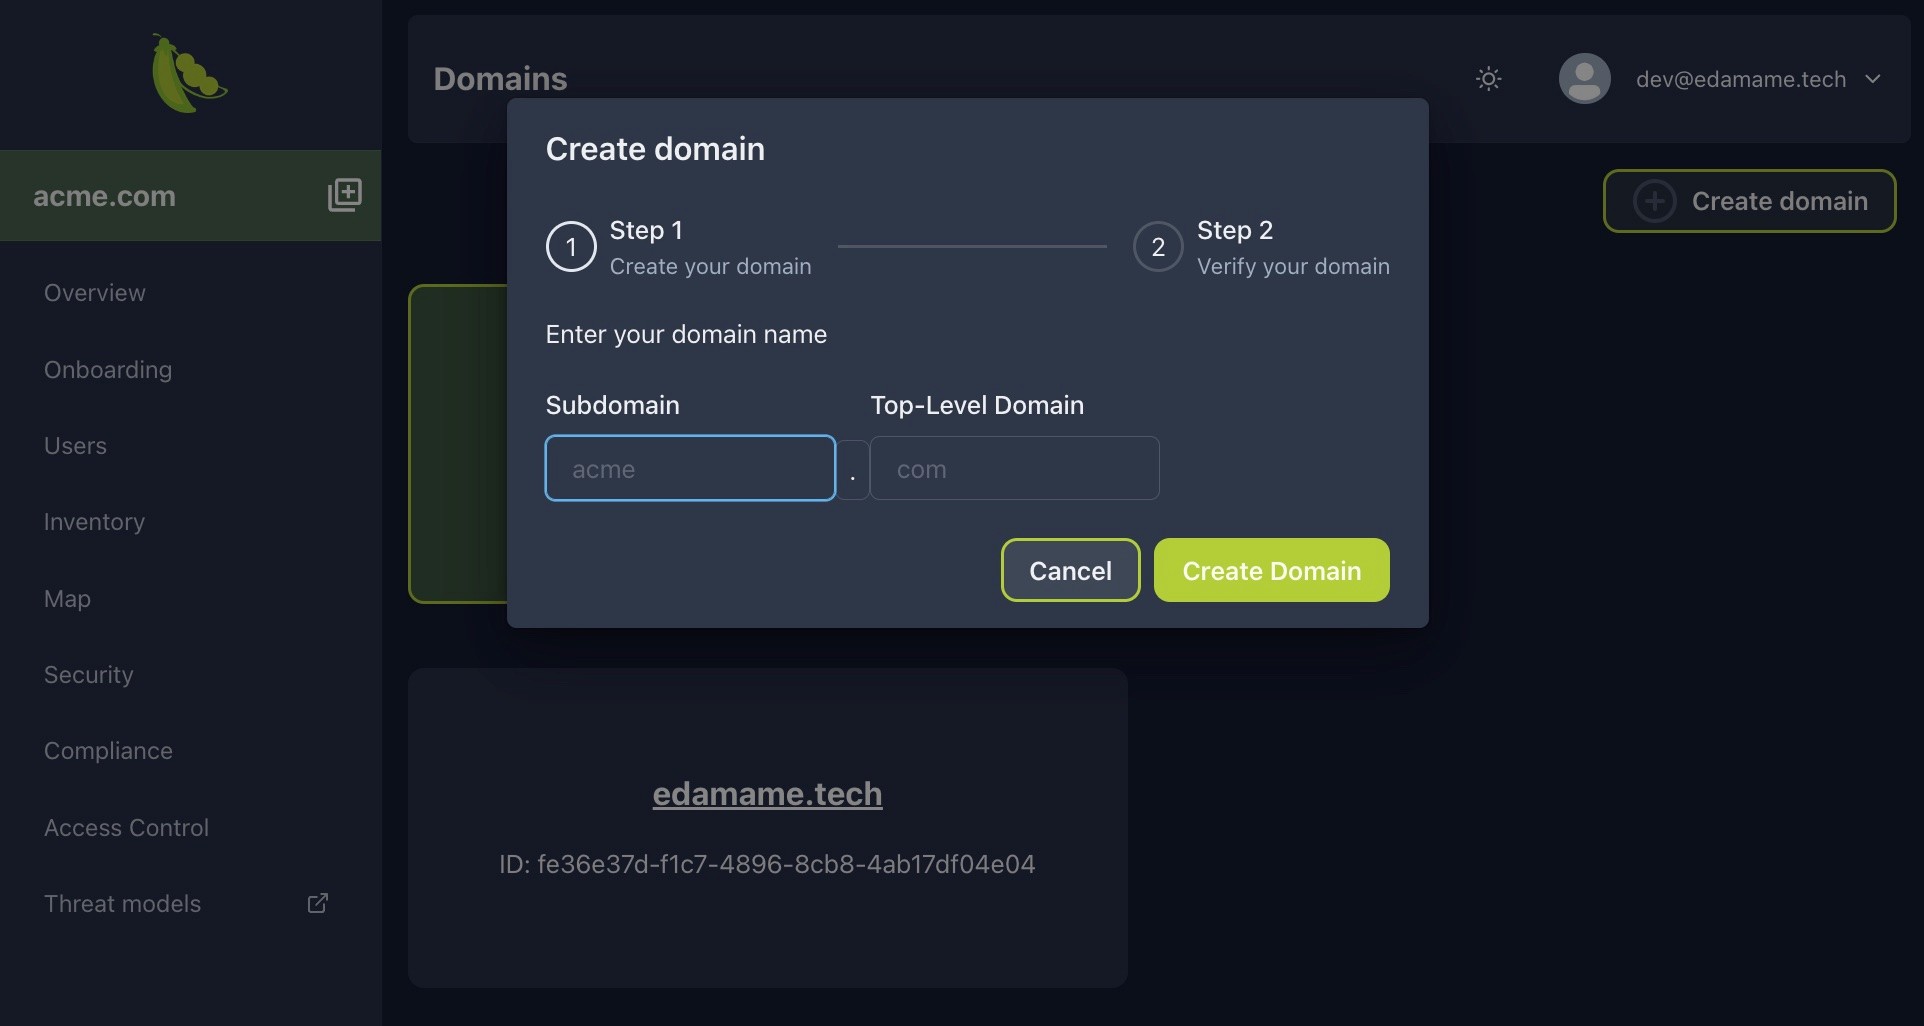
Each device joins your organization with a work email and a one-time PIN, so every address in the named location traces back to a real, verified person.
Continuous device posture
Enforce encryption, patches, EDR, firewall, and integrity. If a device drifts out of compliance, its Microsoft 365 access is revoked in real time.
Native Entra ID enforcement
Use Entra ID Conditional Access named locations and IP allowlists as the enforcement point. EDAMAME keeps them up-to-date for you.
CI/CD & mobile coverage
Apply the same trust model to CI runners, build agents, and mobile devices that interact with Microsoft 365.
Developer-friendly experience
Lightweight agents and clear remediation guidance. Engineers keep their tools and workflows — security runs in the background.
Works with your stack
Runs alongside your IdP, VPN, EDR and MDM, with enforcement through GitHub, GitLab, Entra ID, Google, NetBird, Tailscale, FortiGate and Netskope. No rip-and-replace.
Comparison
EDAMAME delivers the security guarantees of on-prem and air-gapped systems — with the speed and flexibility of modern cloud development.
More than VPNs, air gaps, or IP allowlists.
Alternative
VPN / Tailscale / ZTNA
Once a device connects, it's often fully trusted. Posture checks are sparse, and Microsoft 365 access is not evaluated per request.
With EDAMAME
Entra ID only grants access from the IPs of devices that pass posture right now. No tunnels. No implicit trust.
Alternative
On-prem / self-managed identity
Strong isolation, but difficult for distributed teams, SaaS integrations, and cloud-native CI/CD.
With EDAMAME
Create a virtual air gap around Microsoft 365 and Azure. Only verified devices and identities can reach your tenant.
Alternative
Static IP allowlists
Hard to maintain. Developer IPs change. No visibility into which device is behind an IP.
With EDAMAME
Dynamic, per-device allowlisting. Entra ID only accepts traffic from currently trusted endpoints.
Migration
Roll out Entra ID Zero Trust — without losing control.
Bring Microsoft 365 and Azure under continuous, device-aware Conditional Access — without slowing distributed teams or SaaS integrations.
Step 01
Assess & plan
Discover users, devices, and CI pipelines that reach Microsoft 365. Map risks and target state.
Step 02
Bind identity & devices
Invite developers; each device joins with a work email and a one-time PIN. Establish posture baselines.
Step 03
Enforce Entra ID trust
Turn on dynamic allowlisting and Conditional Access named-location enforcement for Microsoft 365 and Azure.
Step 04
Secure CI/CD
Validate CI runners and build agents before they pull code or secrets.
Step 05
Complete rollout
Extend consistent Zero Trust enforcement across every Microsoft 365 and Azure surface.
Threat Scenarios
Real attacks, blocked by design.
EDAMAME neutralizes the most common supply-chain and credential attack paths — before they reach your code.
Scenario
Stolen personal access token
Without EDAMAME
Attacker uses the token from any device to clone private repos.
With EDAMAME
The attacker’s IP is outside the named location → Conditional Access blocks it, valid token or not.
Scenario
Compromised developer laptop
Without EDAMAME
Malware reads mail and exfiltrates files using existing Microsoft 365 credentials.
With EDAMAME
Posture deteriorates → device automatically removed from allowlist → Microsoft 365 access revoked.
Scenario
Rogue CI/CD runner
Without EDAMAME
Malicious runner pulls secrets and injects backdoors into builds.
With EDAMAME
Runner fails posture or integrity checks → denied before reaching Azure resources or secrets.
Trust & Impact
Security leaders choose EDAMAME to harden their code and pipelines.
Combine the assurance of air-gapped systems with the agility of Microsoft 365 and Azure. EDAMAME lets you enforce Zero Trust without sacrificing developer velocity.
Stop supply-chain attacks at the source — your repos.
Strengthen SOC 2 and ISO 27001 compliance with continuous device-posture evidence.
Win developer trust by making security feel invisible.
EDAMAME gave us the confidence to standardize on Microsoft 365 and Azure with the security guarantees we used to get from air-gapped infrastructure — without slowing our teams down.
VP Engineering
Robotics Company