AI Governance

AI Governance

AI governance for every agent: discover, audit, approve

Cursor, Claude Desktop, Claude Code, Codex, OpenClaw, and Hermes are already on your machines, and every week they reach a new MCP server or tool. EDAMAME discovers every agent from outside the agent, audits each check in the frameworks your auditors use, and lets you approve each new agent, MCP server or tool as a specific, time-limited exception, without switching off the check for everything else. Zero install into the agent. Every observation rolls up to EDAMAME Hub. Security that accelerates humans.

EDAMAME HUB · AI BILL OF MATERIALS
Simulation · all approved
DeviceAgentMCP serverAuthStatus
eng-mac-04Cursorgithub-mcpOAuthApproved
eng-mac-11Claude CodefilesystemLocalApproved
eng-ws-07Claude Codegithub-mcpOAuthApproved
Watching device reports for new agents and MCP servers
AI checks passEvery agent and MCP server listed is approved.
Failing checks map toOWASP AgenticOWASP LLMMITRE ATLASISO/IEC 42001
The AI allowlist is enforced through conditional access at the device's next report.
How AI governance works

From what each machine reports to what you approve

EDAMAME Security and EDAMAME Posture observe every agent from outside it. EDAMAME Hub turns what they report into checks, a score and approvals. Nothing is installed into the agent.

1DiscoverEDAMAME Hub AI Governance, Inventory tab: the agent inventory (AI-BOM) with sandbox state, blast-radius amplifiers, MCP endpoints and secret classes, then agent adoption and governance harnesses

Every agent, approved or not

  • Cursor, Claude Code, Claude Desktop, Codex, OpenClaw and Hermes, wherever they run
  • The MCP servers each agent reaches, and how they authenticate
  • Blast radius: sandbox state, reachable secrets, critical subprocesses, harness detected or not
On each machine, in the app's Agents tabExposureAugmentationEnlightenment
2AuditEDAMAME Hub AI Governance, Overview tab: the AI Governance score, AI posture over time, fleet tiles and runtime findings

Every AI check, in your auditors' vocabulary

  • Each observation becomes a posture check in EDAMAME Hub: agents without a harness, unprotected MCP servers, paused observers
  • An AI Governance score and AI posture over time, for the whole fleet
  • Failing checks map to the frameworks you are assessed on
OWASP AgenticOWASP LLMMITRE ATLASISO/IEC 42001
3ApproveEDAMAME Hub AI Governance, Overview tab: recurring evidence with an Accept button per condition, and the agents and MCP servers not permitted by any allowlist, each with an Allow button

Approve the exception, never switch the check off

  • Accept the specific condition behind a failing check where it is expected; everything else that check covers stays flagged
  • Allowlists name the agents and MCP servers you approve, scoped to a group or a device, with an expiry
  • Restrict a list, and anything unlisted is reported as not permitted
EDAMAME Hub AI Governance, Devices tab: one row per AI-capable device and one column per allowlist, reading Fits or Does not fit
Then enforce

Every device read against every allowlist. Access follows.

  • One row per device, one column per allowlist: Fits or Does not fit, never marked against a list unrelated to its problem
  • Posture-gated conditional access: Netskope, your IdP or your network denies a flagged host the critical resources behind it

An exception quiets alerts and the governance view. Access decisions still follow the check.

See the Zero Trust integrations

Every host, the same evidence

EDAMAME Security runs the pass on workstations. EDAMAME Posture runs it headless on CI/CD runners and any server running AI agents, cloud or self-hosted, OpenClaw and Hermes hosts included.

Governance first, a verdict when you need it

Discovery, audit and allowlists say who runs, what it reaches and what may exist. Agentic Security judges behavior: intent divergence and attack-pattern findings.

Agentic Security

Read the white paper

Start with discovery — inventory every AI agent with EDAMAME Security and EDAMAME Posture, audit each check in your auditors’ frameworks, watch every observation roll up to Hub, and approve the next agent as a specific exception. Add Agentic Security when you need a verdict on behavior.

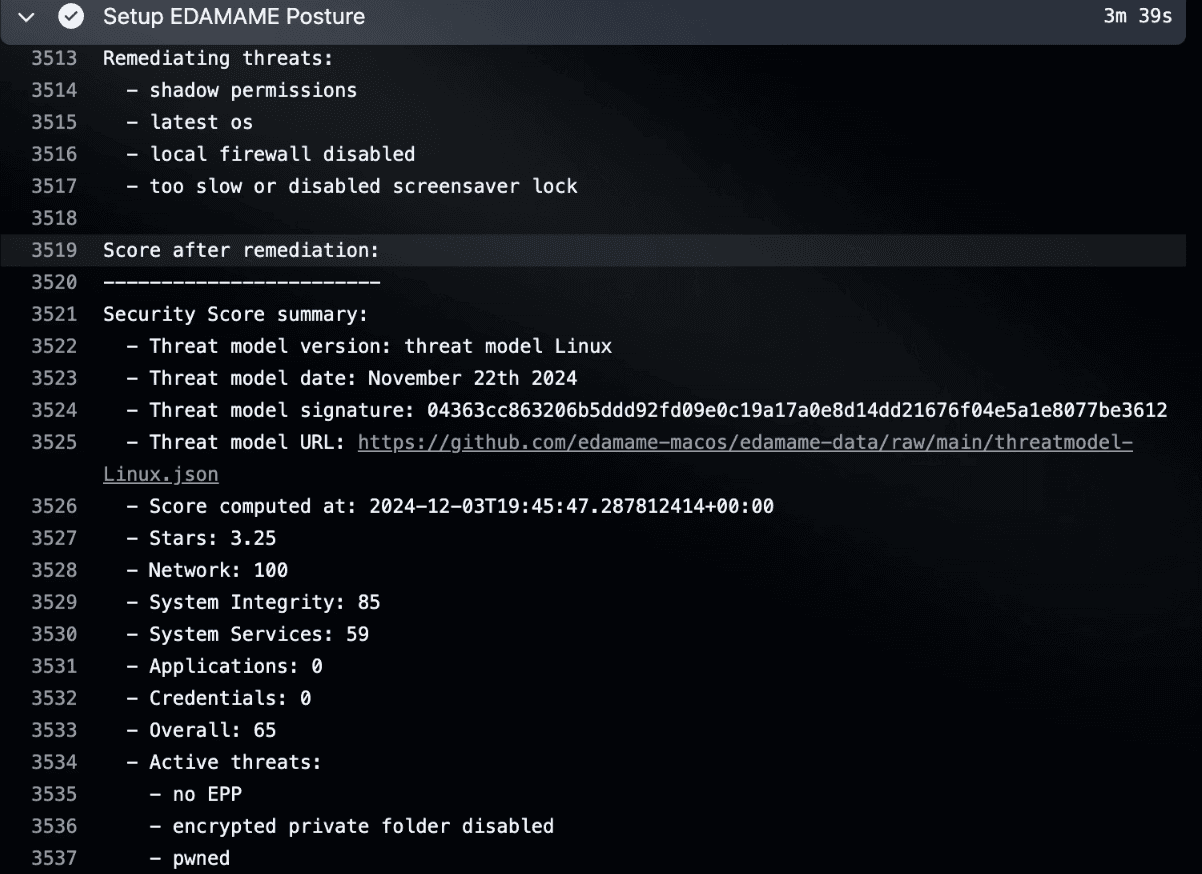
EDAMAME Posture running headless on a CI runner: remediated threats and the security score after remediation

Read the white paper

Start with discovery — inventory every AI agent with EDAMAME Security and EDAMAME Posture, audit each check in your auditors’ frameworks, watch every observation roll up to Hub, and approve the next agent as a specific exception. Add Agentic Security when you need a verdict on behavior.

EDAMAME Posture running headless on a CI runner: remediated threats and the security score after remediation

Read the white paper

Start with discovery — inventory every AI agent with EDAMAME Security and EDAMAME Posture, audit each check in your auditors’ frameworks, watch every observation roll up to Hub, and approve the next agent as a specific exception. Add Agentic Security when you need a verdict on behavior.

EDAMAME Posture running headless on a CI runner: remediated threats and the security score after remediation